We speak OT, not only IT
PLCs, historians, vendor remote access, safety systems: we know these from the inside. We do not apply office IT rules to a control network.
About
We are a specialist practice. We are not a general IT consultancy that added security to its brochure.
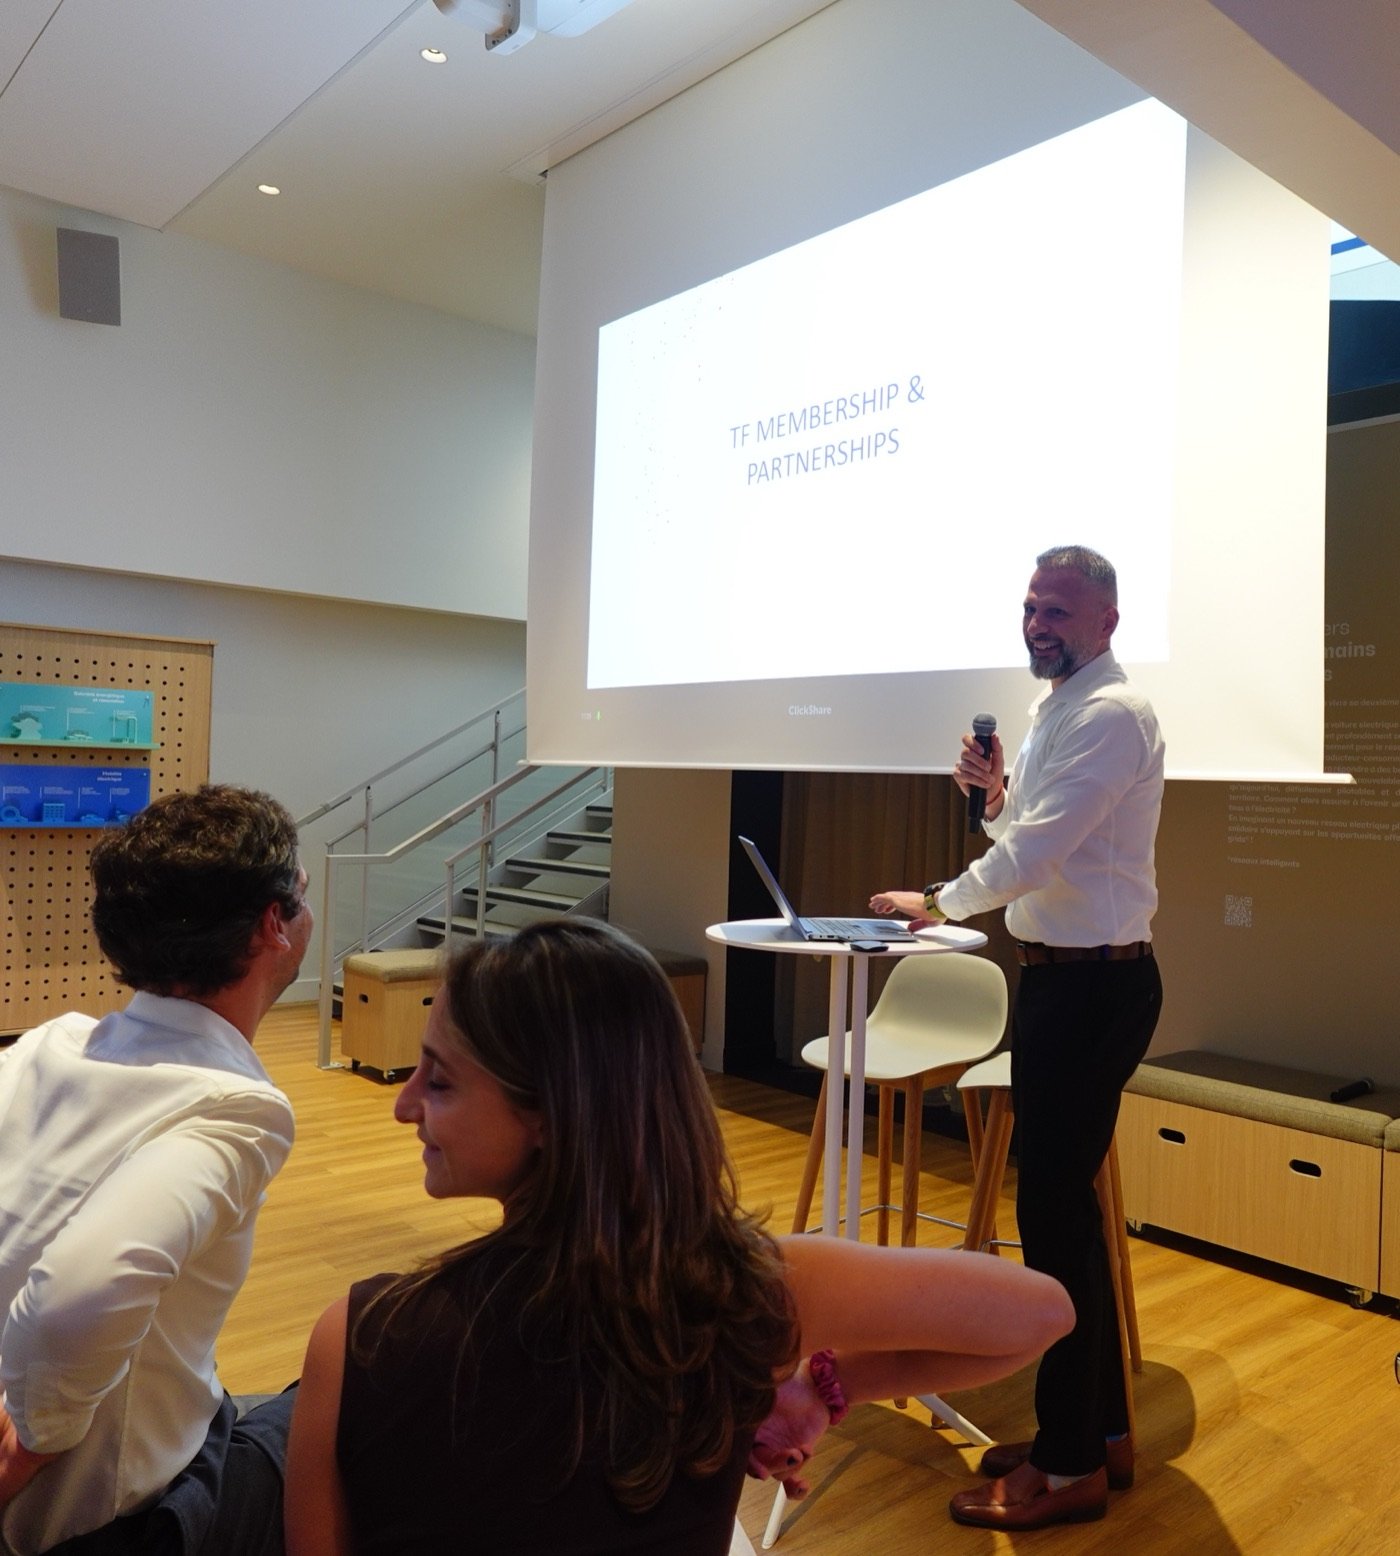
Before founding KIMK, Ivan Dragnev spent 15 years leading cybersecurity inside the energy sector, answering for the risk from the inside. That is the experience every engagement draws on.
The ransomware arrived on a single employee's device at one of our plants. I was cybersecurity manager at an international energy company at the time. Our segmentation held, and nothing crossed the DMZ into the control network. But the IT side went down so quickly that key functions stopped, people could not work, and the plant took significant losses while we rebuilt server after server from backups.
That incident taught me that protecting the control network is not enough on its own. A plant runs on its IT too, and recovery has to be practised before it is needed. Operators accept security that keeps the site running and reject anything that gets in the way of production.
That is why I started KIMK rather than joining a larger firm. Small and mid-sized utilities and producers deserve someone who has lived through an incident, not a checklist and a junior consultant.
Research written with EPRI, and talks at the events where European utilities compare notes.
White paper, EPRI, August 2026
White paper, EPRI, June 2026. How NIS2, the CRA and the Network Code on Cybersecurity change utility cybersecurity, and where applied research can help.
PLCs, historians, vendor remote access, safety systems: we know these from the inside. We do not apply office IT rules to a control network.
NIS2 is the reason for the budget. Resilience is the reason to do the work. We work towards both, and we tell you clearly which is which.
The goal of an engagement is a programme that your team runs. If you still need us for the basics in three years, we have not done our job.
We advise, assess and lead. We are not a managed service or a SOC. We can help you choose one.
If you only need a PDF for a customer questionnaire, a cheaper firm is a better choice.
You probably need more depth, and we would be one of several suppliers. We will tell you this on the call.
Book a 30-minute call. Tell us about your operations. We tell you if we can help, and when we cannot.